Is your phonesystem exposed?
An exposed Asterisk or FreePBX server can run up a large fraudulent call bill in hours. We check yours and tell you exactly what to fix.

01Who it is for
The problems we are usually called about.
Anyone running Asterisk, FreePBX or VICIdial who is not certain when its security was last checked.
A system reachable from the internet
It was opened up for remote workers and never tightened.
Passwords set years ago
Extensions still use the credentials they were created with.
No limits on expensive calls
Nothing stops thousands of calls to premium numbers overnight.
Updates long overdue
Known vulnerabilities remain because upgrades felt risky.
02What we do
What we check.
Network exposure
Which SIP and management ports are reachable, and from where.
Credentials
Weak extension passwords, default accounts and shared secrets.
Call routing
Dialplan paths that could let an outsider place calls.
Fraud limits
Caps on international and premium-rate calling.
Patch level
Known vulnerabilities in the versions you run.
03How it runs
Step by step.
- 01
Scoping call
We agree what is in scope and how we will be given access.
- 02
External check
We look at the system as an attacker would, from outside.
- 03
Configuration review
Accounts, routing, limits and versions are examined from inside.
- 04
Report
You receive findings ranked by risk, each with the specific fix.
- 05
Remediation
We apply the fixes if you want us to, and confirm the result.
04What you get
What you receive.
A written report
Findings ranked by risk, in plain language.
Specific fixes
The exact changes to make for each finding.
Help applying them
If you want us to do it.
Tools we work with
Your stack, not ours
Example build
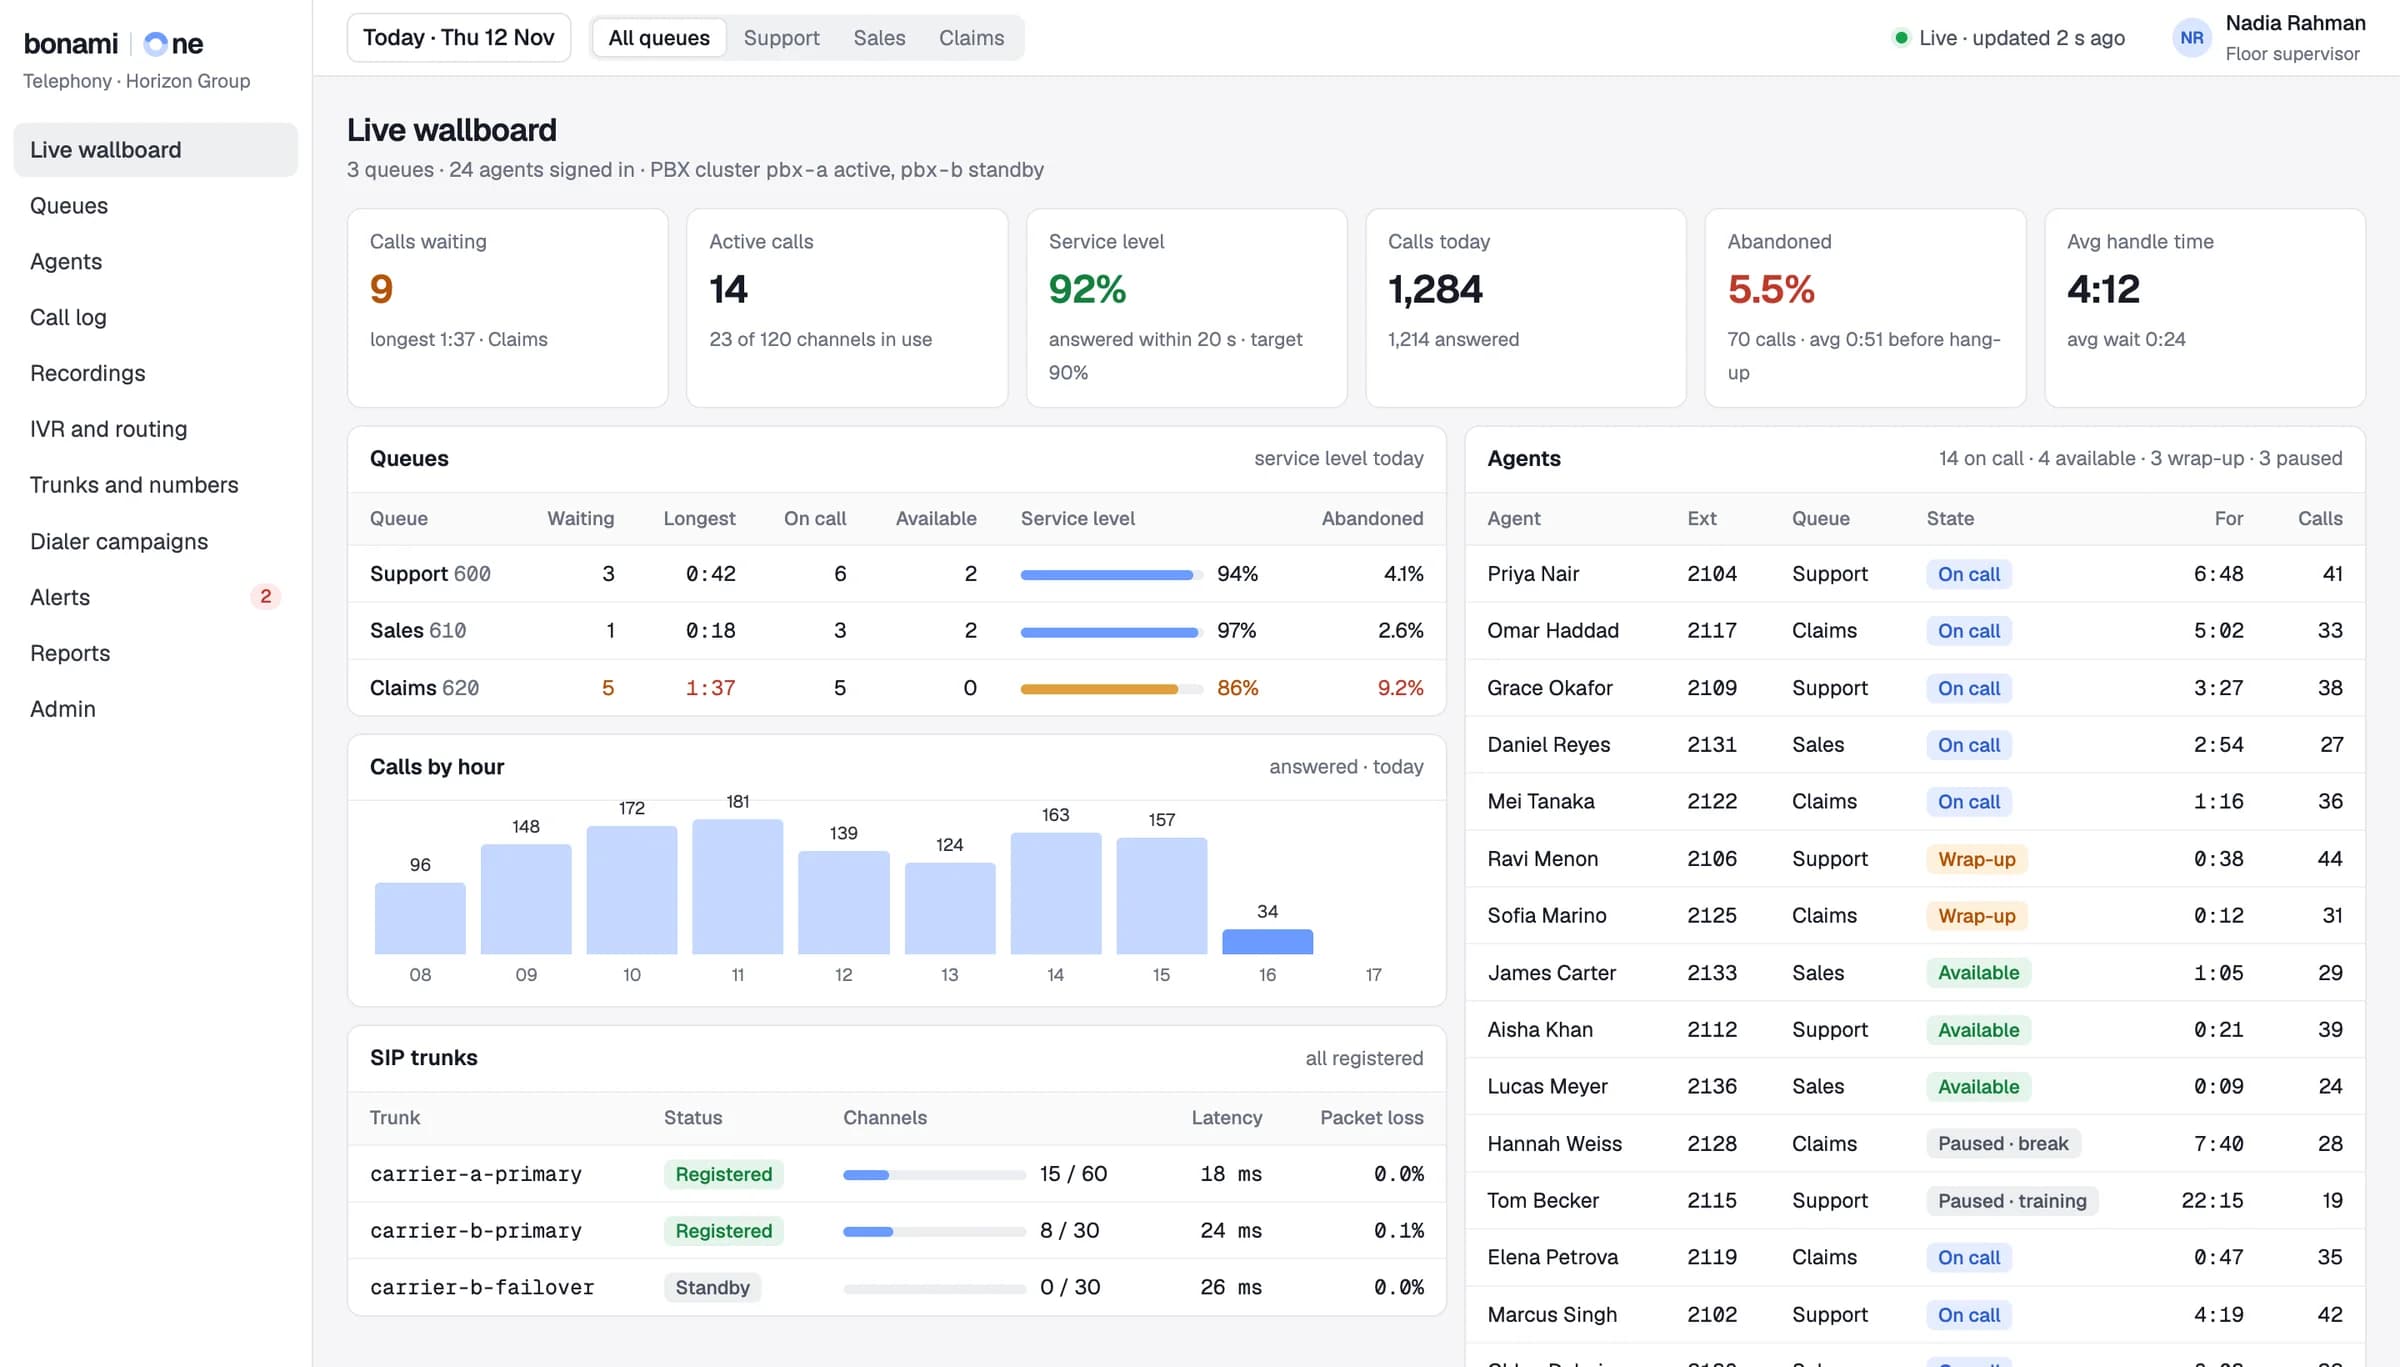
Call-center wallboard
Queues, agents and SIP trunks on one live screen for floor supervisors, driven by Asterisk queue and channel events.
Questions
What clients ask first.
Will the audit interrupt our calls?
No. The checks are read-only and done with care for a live system.
What is toll fraud?
Attackers break into a phone system and use it to place large numbers of calls to expensive numbers they profit from. The owner receives the bill.
What do we receive?
A written report with each finding, its risk and the exact change that fixes it.
Can you fix what you find?
Yes. Remediation can follow straight on from the report.
How often should this be done?
After any significant change, and at least once a year.
What access do you need?
Read access to the system's configuration and the ability to test it from outside. We agree the scope in writing first, and nothing is changed during the audit.
We use a hosted provider. Is this relevant?
Less so. A hosted provider is responsible for their platform. This audit is for systems you run yourself, whether on your own servers or in your cloud account.
How quickly can you start?
Usually soon after the scoping call, once access is agreed. If you suspect you have already been compromised, tell us and we will prioritise it.
Tell us what you run.
Thirty minutes with an engineer. You leave with a clear scope, a timeline and a recommended approach.